
The named security lead for SMEs and startups.
The person your customers, investors and insurers can point to, who knows how companies like yours actually get breached, and who can fix it fast. Without the cost of a full-time CISO.
- CEng
- CITP
- CISSP
- CISA
- CISM
- OSCP
- OSCE
Nobody owns security. Until it goes wrong.
Most SMEs and startups have nobody who owns security. The IT provider does what it is paid for, management assumes someone has it covered, and the first time anyone finds out otherwise is when an enterprise customer sends a 200-question security review, an insurer asks for evidence, or a supplier gets compromised and takes you with it.
I fill that seat without the cost of a full-time CISO. I work hands-on with your team, your IT provider and your management, and I make decisions quickly, based on the practical risks to your business.
How I help
Five ways to work with me. Each one stands alone, and each one leads naturally into the next.
Fractional CISO
A named security lead on a monthly retainer, without the full-time hire. Three retainer levels from a named security lead for questionnaires and insurance through to owning the whole security programme.
Learn moreRisk assessment
Find out how your business would actually be breached and what matters most. An attacker’s-eye exposure review, a risk register you can keep, and a prioritised 90-day plan.
Learn moreIncident readiness
If it happened on Monday, who would decide what? An incident response plan management can actually use, playbooks for ransomware, supplier compromise and payment fraud, and an executive tabletop exercise.
Learn moreSecurity baseline
A working security programme in 30 days. Gap analysis against ISO 27001, SOC 2 or Cyber Essentials Plus, policies, questionnaire answers, insurer evidence pack and roadmap.
Learn moreIncident leadership
Your own independent security lead through a cyber incident and out the other side, working alongside insurers, lawyers and forensics firms, then running the remediation programme afterwards.
Learn moreNot sure where to start?
Thirty minutes on a call and I will tell you which of these you need, and which you don't.
Why me
Senior and hands-on
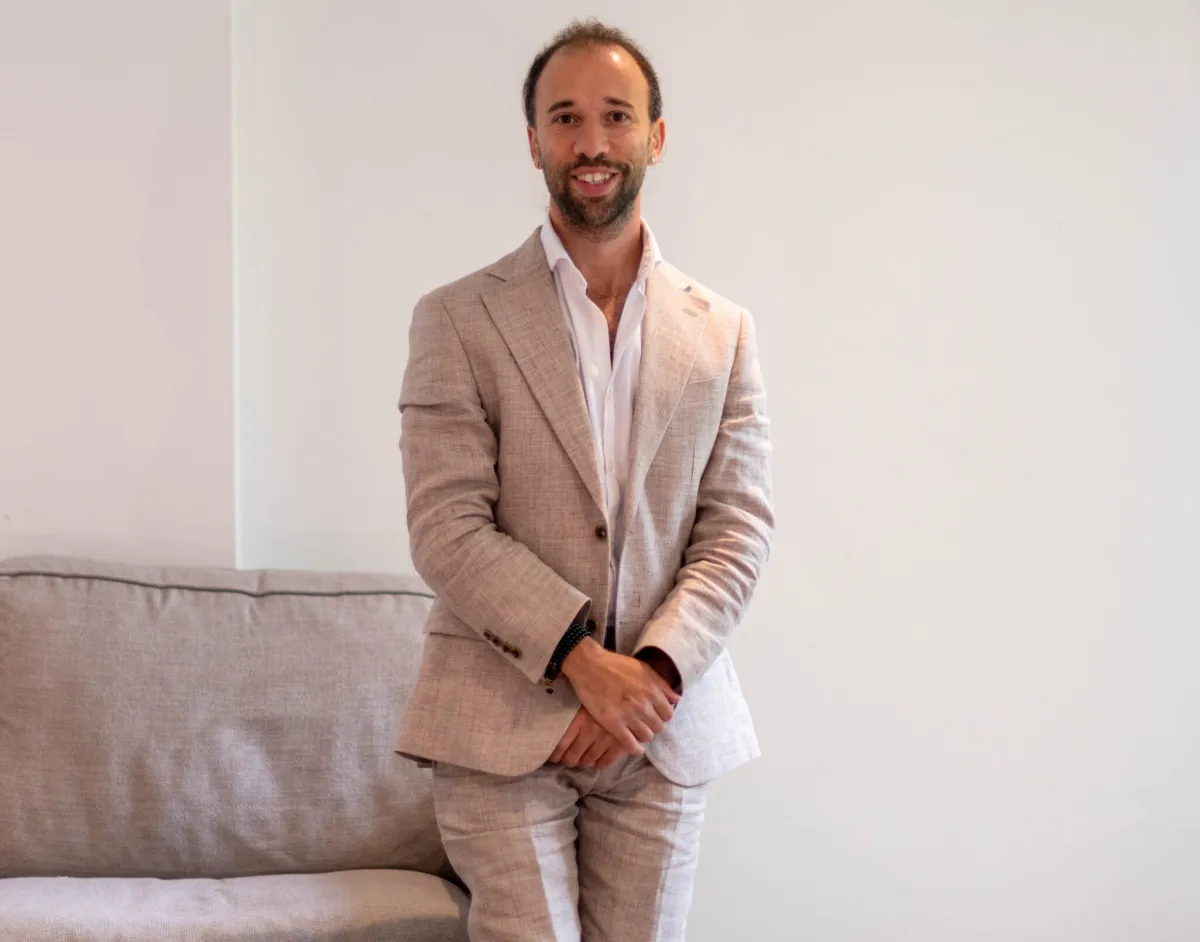
Over 20 years in the field as a CTO, architect and security specialist. Chartered Engineer, Chartered IT Professional, CISSP, CISA, CISM, OSCP and OSCE. I have built and run technical teams and products, and I have broken into and defended them. I don’t hand you a policy pack and leave.
Independent
I am not your IT provider, I don’t resell tools, and I am not your insurer’s panel. My only interest is your business coming out of this well. That is also why your customers, investors and insurers will accept me as your named security lead.
Fast and decisive
You get a straight answer, quickly, about where your real risk is and what doesn’t matter. Fixed fees and monthly retainers rather than open-ended hourly billing, and a stated response time when you need me.
Who I work with
Startups, scale-ups and established SMEs, typically between 30 and 500 people, in the UK, Europe, the US and the Gulf. Companies whose customers, investors and insurers have started asking harder questions than the IT provider can answer.
- Tech and SaaS
- Professional services
- Manufacturing
- E-commerce and retail
- Logistics
- Media
- PE-backed portfolio companies
I don't work in regulated financial services, healthcare, the public sector or crypto. More about how I work.
What clients say
“Adam has a very unique blend of security, development and business skills that made him an invaluable resource to Camelot and extremely effective.”

“Adam provided a first class security penetration engagement for Extreme Networks Professional Services and provided our customer with the relevant information and recommendations to secure their network.”

“From the outset Adam is a man of his word, with utmost integrity, trust and loyalty, and often achieves the impossible with a zealous no excuses approach. A talented IT professional, I recommend him without reservation.”

Also: fractional CTO
I also work as a fractional CTO for startups and SMEs that need senior technical leadership and product delivery. It is where I started, and it is why I am hands-on.
Some of the businesses I have helped





If nobody in your business actually owns security, let's talk.
An active incident, an enterprise customer asking hard questions, an audit coming, or just the nagging feeling. Thirty minutes, no charge, straight answers.